Every attacker, ranked. Every block, approved.
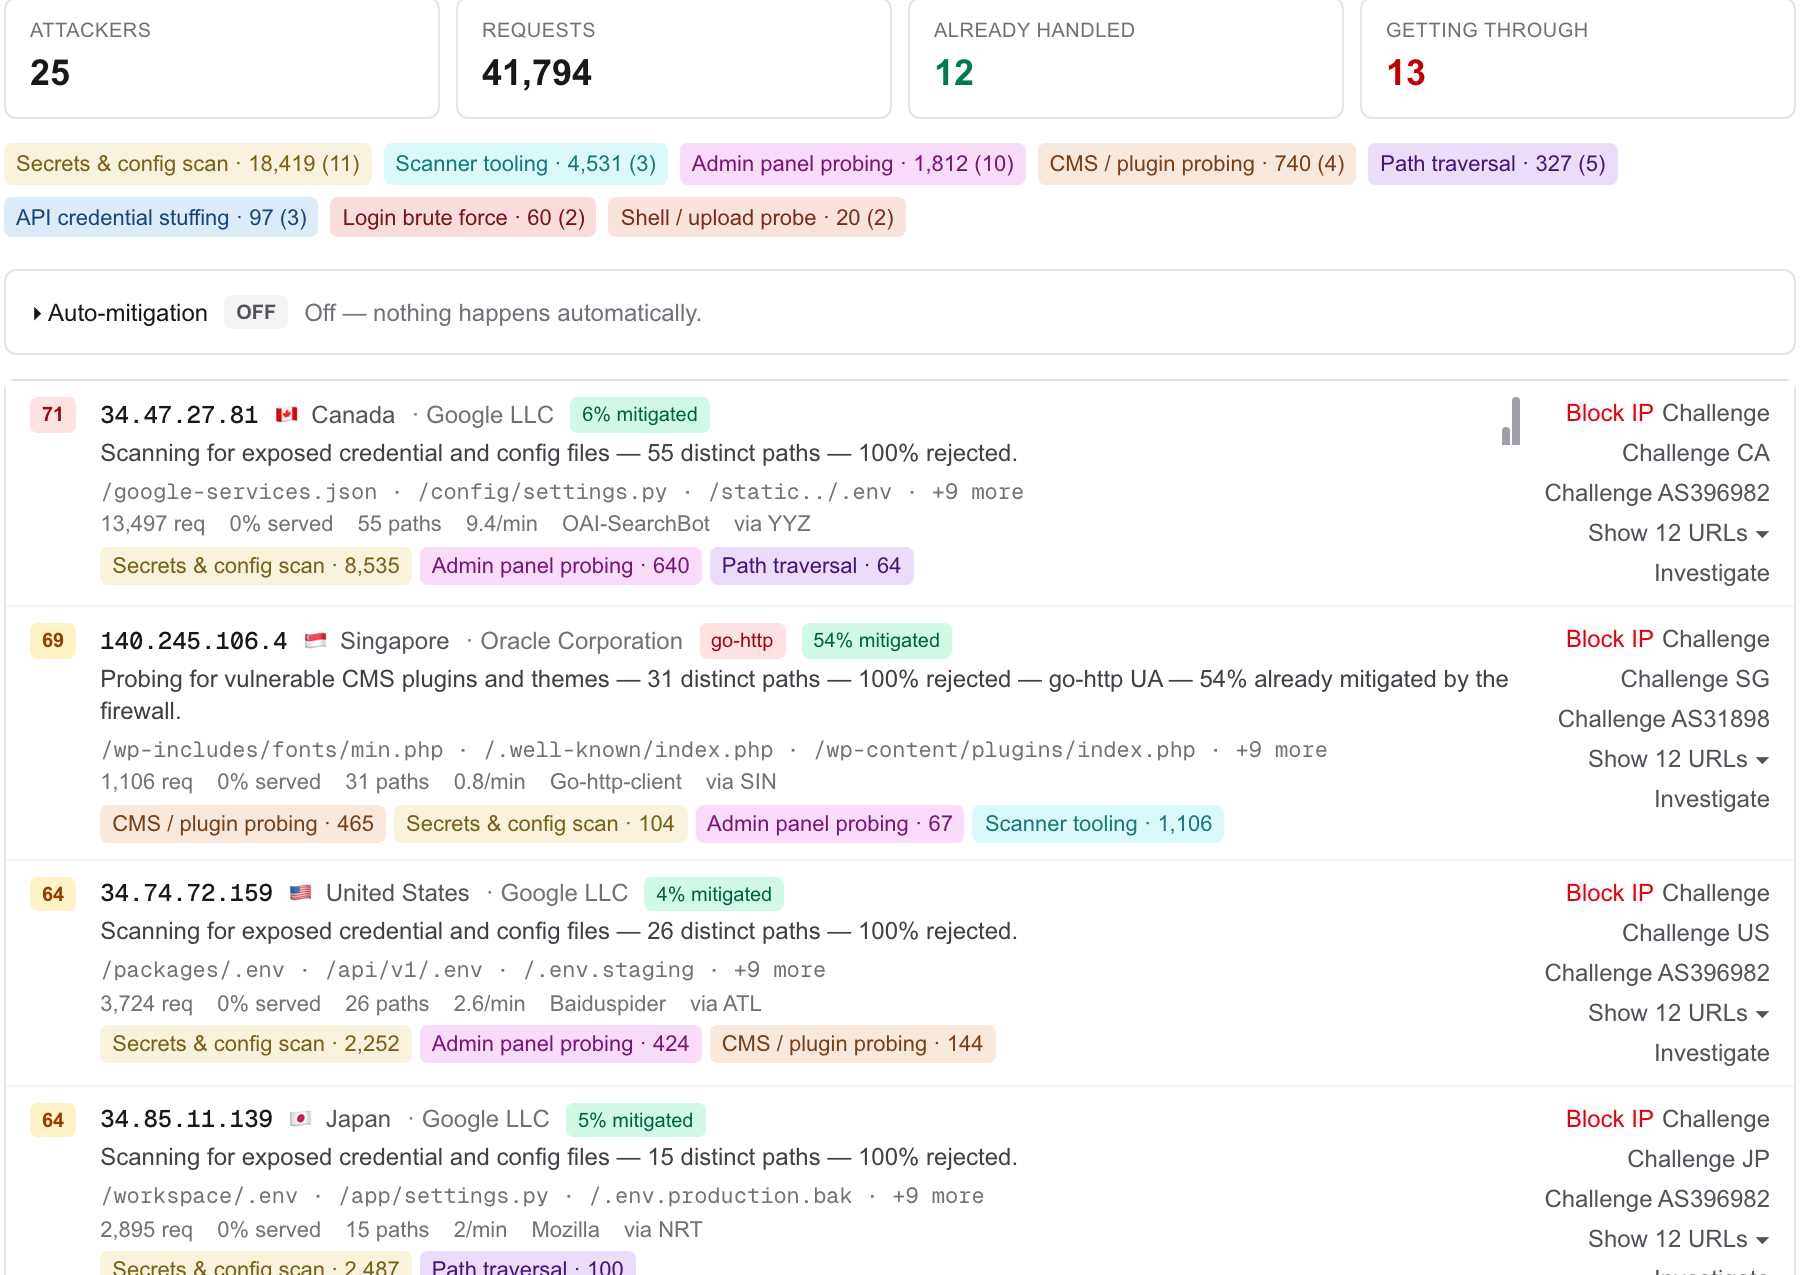
The security tab reads Cloudflare’s firewall and request analytics for all your zones and turns them into a ranked list of sources with a verdict each — then every response is a proposal you approve, not a script that fires.
Who Security engineers, SecOps, SOC analysts, IAM specialists
What gets in the way
- Firewall events across many zones, one zone at a time, with no idea whether the same source is hitting the others
- Blocking that might catch customers, with no count in front of you
- Automation you can’t audit
What Zonesteward does about it
- Attackers scored and categorised
Nine categories, a composite severity, country and network, the paths probed against the paths that exist — and the sources that look hostile but aren’t, with the reason they were cleared. See it →
- Blast radius before the rule exists
A proposed WAF or access rule is run against the last 24 hours of real traffic — broken down by country, network, path and user agent, with the share that was being served — so you see what it would have blocked, and whether that was customers. See it →
- Structural gate, full audit
The model has no write tool. Every change goes through the execution core after a human decision, is read back from Cloudflare, and lands in the audit trail with its revert. See it →
Try asking Who is attacking us right now? · What would this WAF rule actually block?
All roles Agencies & MSPs · Ops & Reliability · Network & Edge · Developers · DNS & IT admin · Leadership · Support